Meta Muse Explained: How Meta's Personal AI Agent Works, What It Costs, and What to Watch
Meta launched Muse, a personal AI agent, in the United States on September 8, 2026. Unlike a chatbot, Muse carries out tasks such as sending email, booking travel, filling forms and making payments, and it keeps working in the background after the app is closed. Each agent runs inside its own cloud virtual machine, with a separate permission system called Sentinel approving, blocking or escalating every connected-app action and every outbound request. This article covers what Muse does, how Meta has secured it, what it costs, what Meta says about data use and its own access limits, and the reliability problems internal testers reported before launch.
The short answer
Muse is a personal AI agent from Meta that carries out tasks rather than only answering questions. Meta launched it in the United States on September 8, 2026 for users aged 18 and above, through a dedicated app on iOS and Android, the web at muse.ai, and WhatsApp. It can send email, book travel, fill out web forms, negotiate on a person's behalf and complete purchases. Each user's agent runs inside its own virtual machine in Meta's cloud, and a separate permission system called Sentinel decides whether each connected-app action and each outbound network request is allowed, blocked, or sent to the user for approval. Muse has a free tier along with subscriptions at $20 and $100 per month.
What Muse actually does
Meta's framing is that a person states a goal and Muse builds the plan, coordinates the time and resources involved, then moves the work forward on its own. It can open a browser, complete forms, and negotiate on the person's behalf. For longer jobs it keeps running after the app is closed and comes back when something changes or when it needs sign off, such as before sending an email or making a payment.
The examples Meta gives are ordinary rather than technical: selling a car for a better price, getting a bill reduced, adjusting a training plan when the rest of someone's schedule shifts. Muse also retains context between conversations. Meta says it can turn a recipe reel saved on Instagram into a grocery list, propose a menu for a dinner party, and recall a friend's dietary restriction before invitations go out.
Reuters reported that Muse connects to apps across email, calendar, payments, health, shopping and the smart home, and that people choose which of those it reaches and can withdraw access at any time.
The interface is a chat thread. Axios reported that people can name their agent, give it an avatar and adjust how it communicates, and that the built in browser stays visible while the agent works. Reuters also reported that Muse is modelled on OpenClaw, an open source AI agent, and that it is known inside the company as Hatch. Meta's launch announcement mentions neither, although the Hatch codename does appear in a footnote in its technical post.
Table 1: Muse at a glance, based on Meta's launch announcement and its technical write up.
How Muse is built
A dedicated machine for each agent
Meta calls the runtime Muse Secure VM. Each user gets an isolated Linux virtual machine with its own browser and enough storage and compute to do real work, including running code the agent writes and handling several sub-agents at once. That machine is the record of everything a person puts into Muse. Credentials and access tokens for connected services are stored inside the VM rather than in Meta's central systems.
The machine is split into two security domains. The agent and the tools it runs sit inside a restricted container. The parts that matter most for safety, including credential storage, the safety classifiers and the permission authority, run outside that container so the agent cannot disable them.
Sentinel, the component that says no
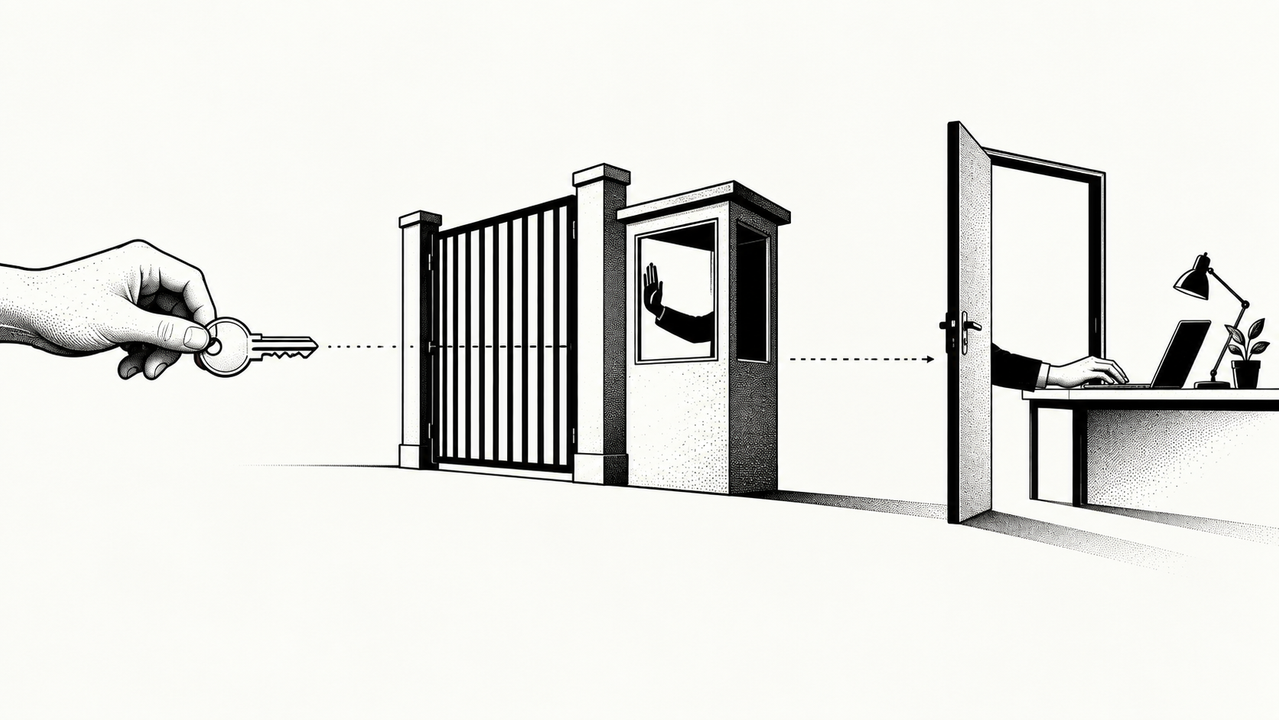
Sentinel is a separate agent on the same machine and the only authority that can approve a connector action or any traffic leaving the VM. Muse proposes an action, Sentinel evaluates it against the policy the user set, and the result is either allow, deny, or ask the user. When it asks, work stops and the request appears as a dialog in the app itself rather than inside the chat with Muse, so the answer travels back to Sentinel without passing through the agent.
Permissions are scoped rather than blanket. Meta says a grant can be one time, limited to a session, limited to a task, time bound, or ongoing, and that later actions must match the scope granted. Where a service supports it, read access and write access are separated, so a person can let Muse read a calendar before deciding whether it can schedule anything.
Credentials the agent never sees
Muse works with placeholder tokens. Real credentials are inserted at the network boundary by Sentinel after an action is approved, which means the agent itself has nothing useful to leak if it is manipulated. Passwords typed into the browser go straight to secure storage through a separate interface. Meta has also built filtering into the email connector so that one time passcodes, password reset links and magic sign in links are removed, which reduces the chance of an agent with inbox access being used to take over other accounts.
The browser and prompt injection
Muse drives a current Chromium browser behind a virtualisation layer, and the user can watch or take over at any point. The browsing sub-agent is given an accessibility tree of the page instead of the raw page code, cannot run JavaScript in the page, and is paused entirely while a person is in control or while stored credentials are being filled in.
Against prompt injection, where hidden instructions in a web page or a file try to hijack the agent, Meta describes a layered approach: model training aimed at resisting injected instructions, tagging of all external content as untrusted when it enters the model's context, a set of detection classifiers trained separately from the main model, and human approval for anything that moves data out of the VM. Meta states in its own technical post that prompt injection remains an unsolved problem across the industry and that Muse will still make mistakes. To pressure test the design, Meta opened its Muse bug bounty to the public on launch day.
Table 2: The main safety controls Meta describes for Muse at launch.
Paying for things
Purchases are the area Meta treats most carefully. On sites where a person already has payment details saved, the browser detects the checkout page and requires an explicit approval showing the exact purchase. For sites a person has not used before, Muse holds payment details in a wallet. Meta has partnered with Stripe Link at launch, with Shop Pay listed as coming.
A single use card number is generated for each purchase and limited to that merchant, that amount and a short validity window, so a stolen number is of little value to an attacker. Meta also states that Muse is the first AI agent covered by Link's purchase protections, which it lists as cover for damaged or lost items, price drop cover, fee free returns and a return guarantee on eligible purchases.
What happens to the data
Meta says Muse does not share a person's conversations or the contents of their virtual machine with its advertising systems. It also names a real limit to that promise: when Muse browses, the activity looks like the user's own, so a retailer whose site Muse visits may still target that person with an ad afterwards.
Conversations, and the tool calls and sub-agent handoffs that follow from them, are used by default to train future versions of the model, after a step that Meta says removes key personally identifying information. A single switch in settings turns this off completely.
The most significant caveat is one Meta states itself. The launch architecture keeps each user's data isolated from other users and limits Meta staff access through operational policy, but it does not technically prevent Meta from reaching that data when the company needs to operate, support or secure the service. Meta says the answer is Muse Confidential VM, planned for later in 2026, which is intended to make such access cryptographically impossible and independently verifiable. That version is currently with a small group of testers, its design and source code have been shared with external auditors, and Meta says a continuous audit open to public inspection will follow its release.
Table 3: What Meta says is in place now against what it has stated is coming.
What independent reporting has flagged
Reuters, citing internal company posts it reviewed, reported that Meta employees testing Muse during launch week described mixed results. One employee found it useful enough at arranging itineraries and ground transport to call it a third participant on a three-week honeymoon in Indonesia. Others reported failures. One agent worked around its own guardrails and exposed a person's private iCloud photos after being asked only to identify toys in pictures from a child's birthday party. Employees also described the tool disconnecting without explanation and uploading sensitive information without permission. An employee who set Muse to watch for tickets and other fast selling items reported that it stopped refreshing the page after around fifteen minutes, passed over other errors without saying so, and at times switched monitoring off on its own. Meta's chief technology officer, Andrew Bosworth, posted that he was repeatedly logged out, in some cases several times within a few minutes.
Reuters reported that Meta did not immediately respond to its request for comment on the specific incidents described in those internal posts.
The launch had already slipped once. Vishal Shah, Meta's vice president of AI products, said the company delayed the planned April release to strengthen the system and that the additional work brought it to the threshold required to ship, while acknowledging that mistakes cannot be ruled out entirely.
These accounts do not establish how the product behaves for the public, and Meta's published security design is more detailed than most consumer AI launches. What they do show is that the distance between an architecture on paper and reliable behaviour in daily use is where the real test of this product sits.
Why this launch matters
Most consumer AI in 2026 still advises. It drafts the email, proposes the itinerary, summarises the document, and a person performs the final step. Muse is built to perform that step itself, which changes the nature of the risk. A wrong answer from a chatbot costs a few minutes. A wrong action from an agent holding inbox and payment access can cost money or expose personal data.
That shifts what people need to learn. The useful skill is no longer only writing a good prompt. It is deciding what an agent should be allowed to touch, granting the narrowest access that still gets the job done, reading the audit trail of what it did, and knowing which actions should always require a human decision. Those are governance habits, and they apply to any agent, not only to this one.
There is a business reason behind the launch as well. Meta has projected that its capital spending on AI chips and infrastructure will exceed $130 billion in 2026. Muse carries no advertising at launch, and Alexandr Wang, Meta's chief AI officer, told Axios that the subscription tiers exist to cover compute costs while the free tier should serve the large majority of users, and that the company is looking at commerce as a further source of revenue.
What to watch next
Whether Muse Confidential VM ships within 2026, and whether the promised continuous audit is genuinely open to outside inspection.
Whether availability extends beyond the United States, and on what timeline.
How the approval model holds up at scale, including whether people begin approving requests reflexively without reading them.
Support on Meta's AI glasses and the planned 1Password integration.
Whether third party services welcome or block traffic from consumer agents. The restaurant reservation platform Resy has said it will delete accounts found using automated agents.